
 Share
 Print
|
|
|
|
|


Corrosion Level Authorization Group Explorer
The Corrosion Level Authorization Group Explorer allows the System Administrator or other designated users to manage which users are in each specific Corrosion Level Authorization Group. Users are added or deleted from Corrosion Level Authorization Groups who are listed in the screen below.
The user may use the Corrosion Level Authorization Group System Transaction Code to define who is allowed to be part of the authorization process via the Corrosion Level Authorization Group Explorer. Within this window, two sections will be displayed. On the left, a list of the existing Authorization Groups created through the transaction code, and the users/employees assigned to the group(s) when expanded. On the right, a complete listing of the users/employees expanded from their designated User Profile.
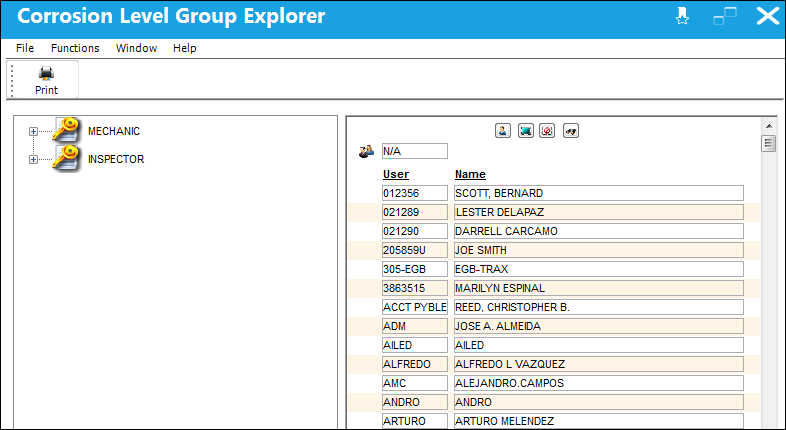
In the Corrosion Level Authorization Group Explorer window, users are categorized by the Adopted Group Profile they belong to in the Security Explorer. This is configured for each individual user, and if they are not associated to any Adopted Group Profile, then they fall into the 'N/A' Group Profile by default. For additional information regarding Group Profiles, refer to the System Administration Training Manual.
To add a user or users to a Corrosion Level Authorization Group, begin by highlighting the ID/Name(s) to the right. Select the User  icon and drag it to the selected Authorization Group. Either individual or multiple users can be added at the same time to a specific Corrosion Level Authorization Group. When adding multiple users at the same time, highlight all of the required users. The Select All
 option can be used if all users are going to be selected.
The ability to find a specific user can be accomplished by selecting the Find  button. This is extremely helpful when searching through a large number of users for one specific user.
Once the user(s) are dragged and dropped on the specific group on the left pane using the User icon, the following pop-up message is displayed:
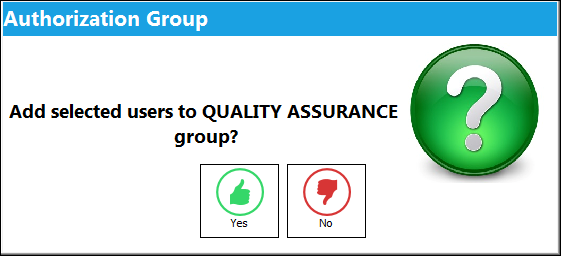
Select 'Yes' to add the highlighted user(s) to the Corrosion Level Authorization Group. Select 'No' to return to the screen with no changes made.
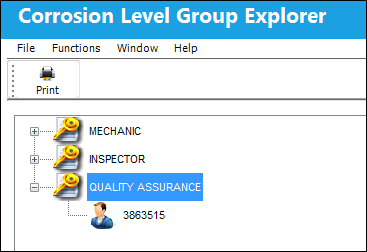
If 'Yes' is selected, then TRAX re-displays the above screen with the new user(s) listed in the applicable Corrosion Level Authorization Group.
To remove a user from a selected Authorization Group, right-click on the user's name. Select 'Remove User' from the pop-up:
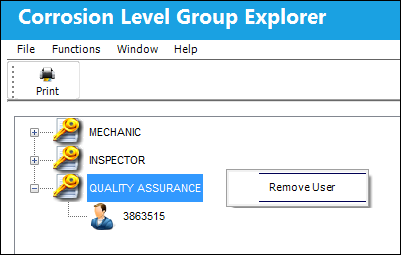
Select Yes when the following pop-up message appears to remove the user(s) or No to return to the screen with no changes:
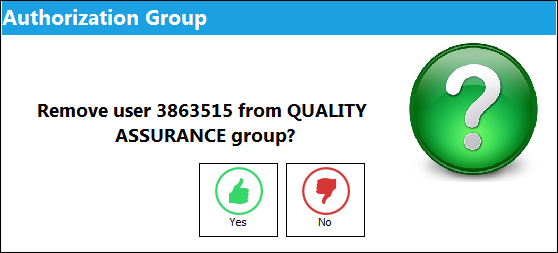
If Yes is selected, TRAX re-displays the Corrosion Level Authorization Group Explorer window without the selected user in the applicable Corrosion Level Authorization Group.
Share
Print
|
©1997-2026 Trax USA Corp. All rights reserved. This manual may not be copied, photocopied, reproduced, translated, or converted to any electronic or machine-readable form, in whole or in part, without prior written approval from Trax USA Corp. |
 |